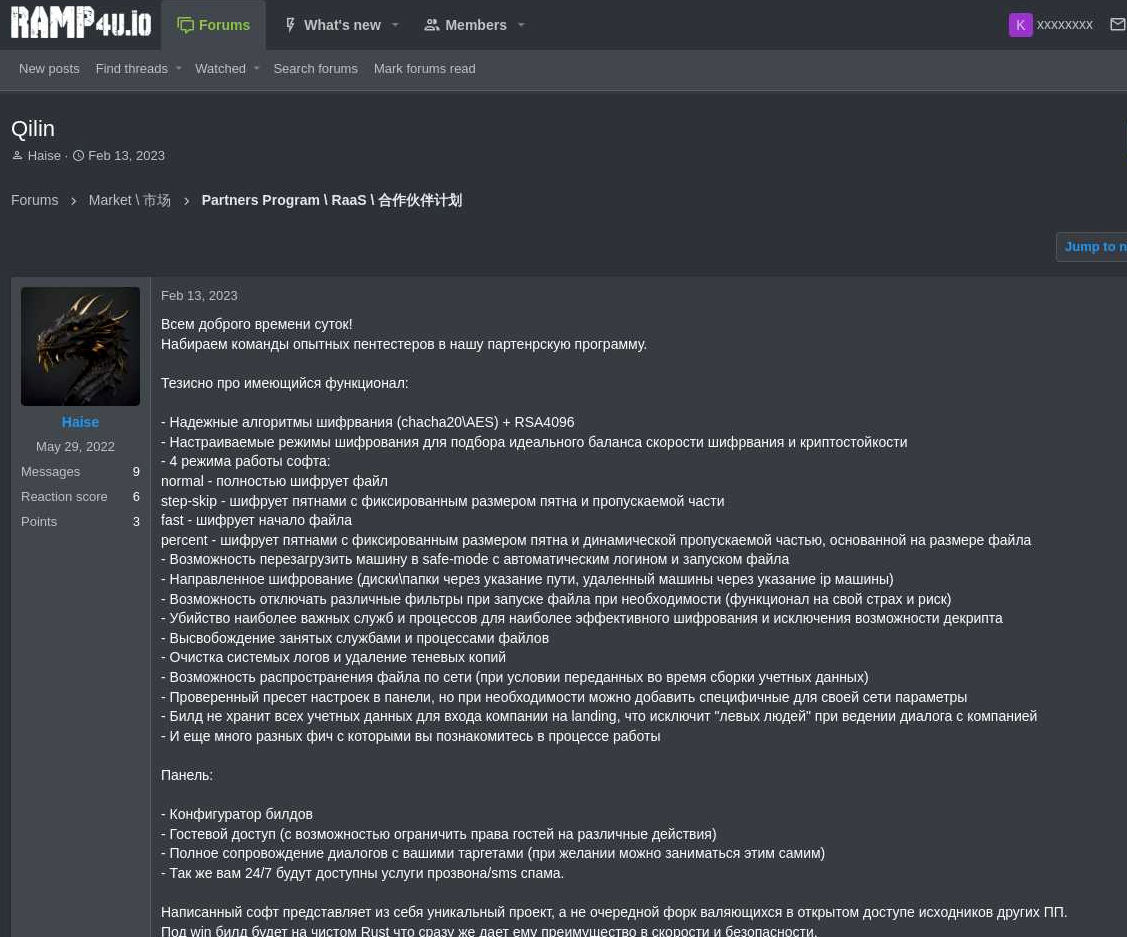
The ransomware group Qilin has been identified as the world's most active ransomware affiliate program, with operators claiming at least 365 victim organisations in the three months leading up to November 2026, according to Krebs on Security.
A ransomware affiliate program is a business model in which a ransomware developer licenses their malware to other cybercriminals. Affiliates carry out the attacks, while the operator provides the software, infrastructure, and support, with profits shared between them. This model has become dominant because it lets skilled developers operate remotely while less technical criminals handle intrusion and extortion.
The investigation points to a 36-year-old man living in St. Petersburg, Russia, as the administrator of Qilin. The identification stems from operational security mistakes made over the last decade, including errors that linked the administrator's online activities to his real identity.
The report is based on a summary of findings, and the full details have not been independently verified by VANTIX. It remains unclear whether law enforcement has been notified or whether any charges have been brought against the identified individual.


