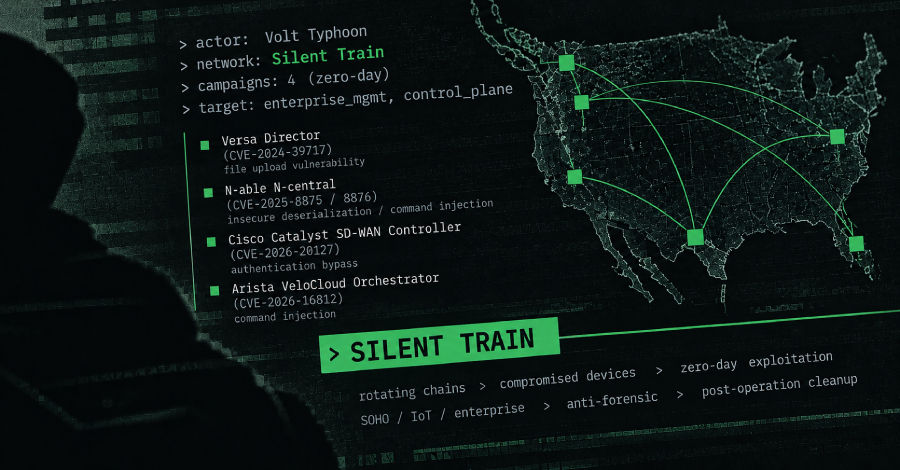
Volt Typhoon, a China‑linked cyber espionage group, used a covert access network called Silent Train for zero‑day exploitation and strategic access, according to a Lumen Technologies Black Lotus Labs report. The network, first identified in late 2023, relied on rotating chains of compromised SOHO, IoT and enterprise infrastructure, and has since been disrupted.
What It Means for Readers
Readers can see that the removal of Silent Train eliminates a ready‑made platform the group used to launch undisclosed exploits, which may reduce the frequency of its zero‑day attacks. However, the group still possesses other compromised devices, so the impact is limited to this specific network.
What Remains Unknown
Details such as the exact number of victims, the specific zero‑day vulnerabilities exploited, the full list of compromised devices and the timeline of the four campaigns have not been disclosed.
VANTIX Takeaway
The takedown of Silent Train shows that coordinated action can disrupt a covert espionage infrastructure, but Volt Typhoon may simply shift to another chain of compromised systems.


