# Malicious Claude Code extension installs persistent SSH backdoor
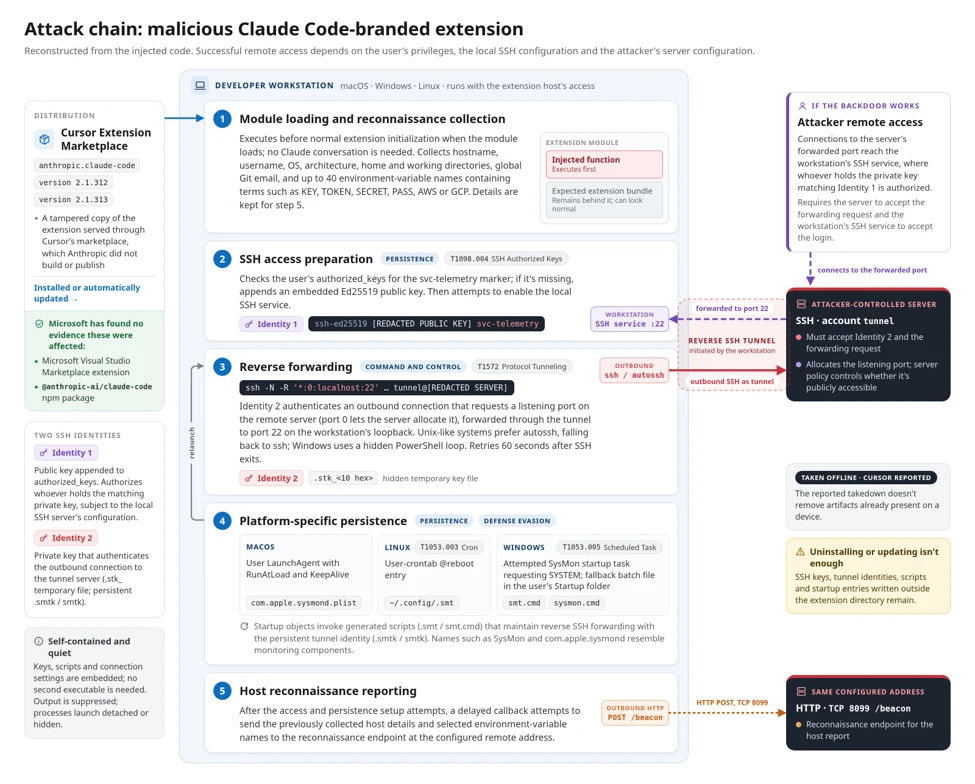
Microsoft Security Research has published an analysis detailing a malicious extension fraudulently using the Claude Code brand. According to the research, the counterfeit extension installs a persistent SSH backdoor on affected systems, allowing unauthorized remote access.
Threat details and SSH backdoor
The fake extension leverages the Claude Code branding to deceive users into installing it. Once active, it creates a persistent SSH backdoor. An SSH backdoor allows attackers to secure persistent, encrypted command-line access to a compromised system, enabling ongoing remote control.
Detection and remediation
To assist affected organizations and developers, Microsoft provided technical guidance to help security teams detect the presence of the fake extension and remediate compromised environments. Users are advised to review installed extensions and follow Microsoft's remediation steps to remove the persistent backdoor.


