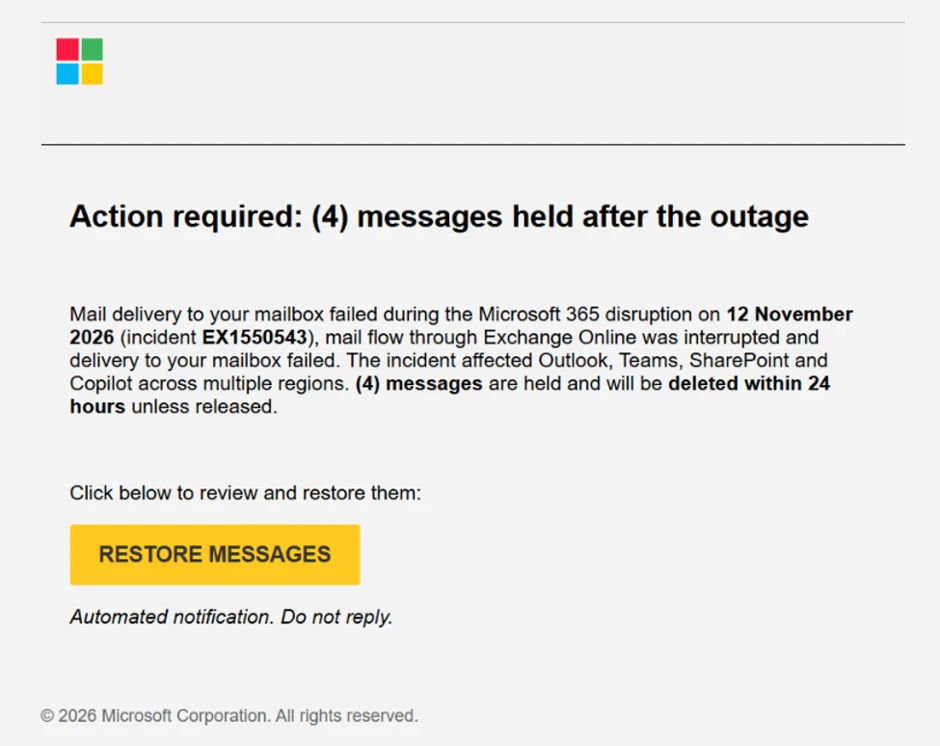
What happened
Microsoft Threat Intelligence has identified a high‑volume phishing campaign that uses fake Microsoft 365 outage alerts to lure organisations across multiple industry sectors worldwide.
How the scam works
The attackers send messages that claim Microsoft 365 is down and ask recipients to click a link or open an attachment to restore service. The links lead to malicious sites designed to steal credentials or install malware.
Scope of the attack
The campaign targets a range of industries and reaches users in many countries, showing a broad global reach. Microsoft notes the volume of messages is unusually high.
What remains unclear
The article does not specify the exact number of victims, the specific lure content, or any follow‑up actions by Microsoft.
The blog post was published on 16 November 2026. The campaign leverages the perception of an outage to create urgency.


