What Happened
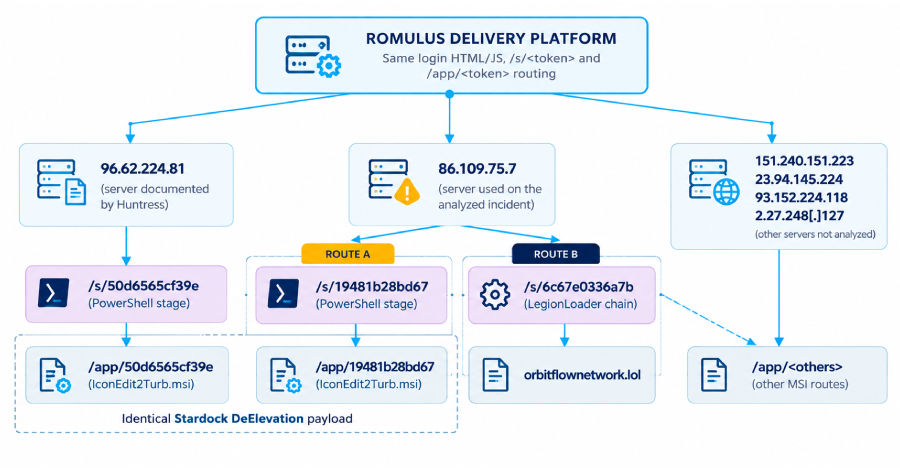
Cybersecurity researchers from Forescout Research - Vedere Labs have disclosed details regarding a new malware distribution platform named ROMULUS. The system operates as a malware-as-a-service delivery platform that employs ClickFix-style social engineering lures on fake landing pages, tricking unsuspecting internet users into manually executing commands that infect their own computers with malware, including LegionLoader.
Key Details of the ROMULUS Campaign
- Delivery Mechanism: Rather than relying solely on traditional software vulnerabilities or direct file downloads, ROMULUS leverages ClickFix tactics. These attacks present visitors with fake browser errors, CAPTCHA prompts, or verification screens that instruct users to copy and paste code into their command line or terminal.
- Payload Distribution: When a user executes the deceptive commands provided on the landing page, the script retrieves and installs malware such as LegionLoader onto the victim's device.
- Service Model: Forescout Research - Vedere Labs describes ROMULUS as a delivery service for threat actors, enabling attackers to deploy fake landing pages and efficiently distribute multiple malware families.
Why It Matters
ClickFix attacks exploit human behavior rather than software flaws. By convincing users to manually copy and execute terminal commands, attackers can frequently bypass conventional web browser security prompts and automated file scanners that typically inspect downloaded files.
What It Means for Readers
- For Everyday Internet Users: Be extremely cautious of any website claiming your browser has an error or demanding that you copy code or press key combinations (such as Windows Key + R) to solve a problem or verify you are human.
- For IT & Security Teams: Educate employees about ClickFix vectors, as user-executed terminal commands remain a rapidly growing tactic for initial access across corporate and personal environments.
VANTIX Takeaway
ROMULUS demonstrates how cybercriminals are increasingly leaning on user-driven execution tactics to deliver payloads like LegionLoader. Treating any web page request to run command-prompt scripts as an immediate threat is essential to remaining safe.


