What Happened
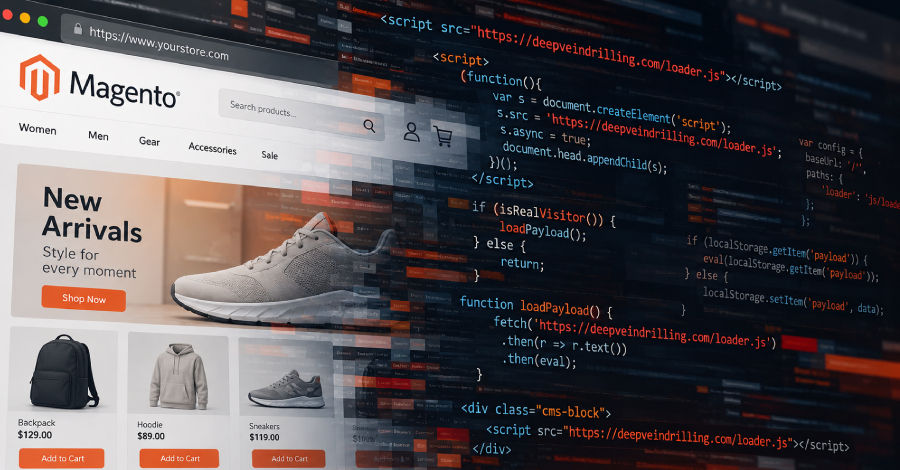
Dutch e-commerce security company Sansec has discovered a long-running cyber campaign that has compromised 953 online stores. Active since July 2025, the attack primarily targets e-commerce platforms running the Magento content management system (CMS).
The Key Details
The campaign relies on stealthy injection techniques designed to bypass security monitoring:
- Targeting: The vast majority of infected storefronts are powered by Magento.
- Infection Vector: Threat actors inject small code snippets directly into store pages, which then load malicious JavaScript loader code through Magento CMS blocks when customers visit the site.
- Detection Evasion: The malicious code is specifically crafted to evade conventional security scanners, allowing the campaign to persist unnoticed across nearly 1,000 stores over more than a year.
Why It Matters
Digital skimming and unauthorized script execution pose a direct threat to online retail security. By injecting loader scripts into internal CMS blocks rather than relying on external script references, attackers can execute malicious payloads while hiding from standard automated scanners. This makes detection significantly harder for merchants relying solely on routine surface scans.
What It Means for Readers
- For E-commerce Merchants: Store administrators—particularly those operating Magento storefronts—should conduct manual inspections of CMS blocks, database entries, and theme files alongside automated scanning.
- For Developers and IT Teams: Security reviews must extend to database integrity checks and content management blocks to catch stealthy injections.
- For Consumers: While shoppers cannot see server-side CMS injections, using payment methods with active fraud protection or virtual cards provides an extra layer of financial security.
VANTIX Takeaway
Automated security scanners are an essential line of defence, but stealthy attacks like this demonstrate why store owners must conduct direct database and CMS block audits to ensure site integrity.


