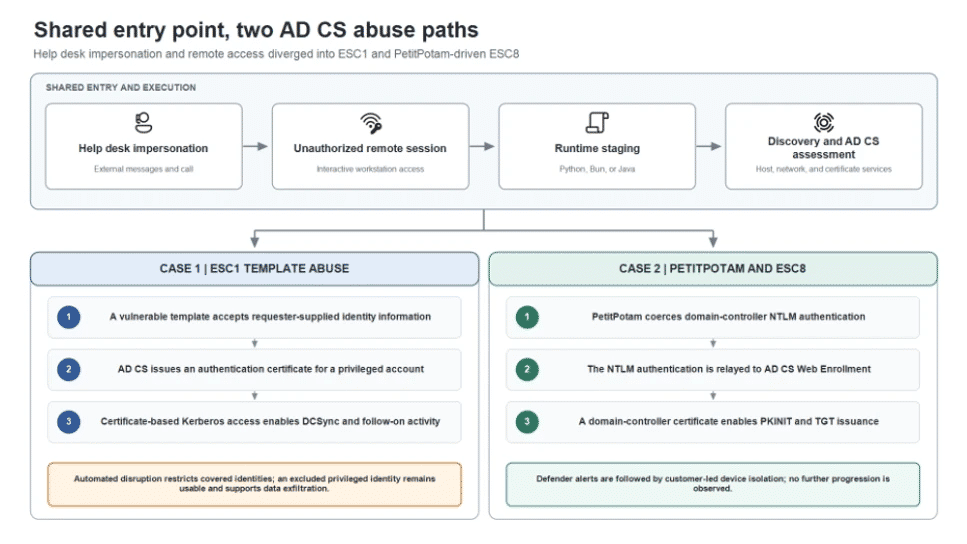
Microsoft Security researchers have documented an attack chain from help desk impersonation to Active Directory Certificate Services abuse. The investigation by Sagar Patil, Jesse Birch and Tal Tzhori was published on the Microsoft Security Blog on 30 October 2026.
The confirmed path begins with an attacker impersonating Teams support to gain remote access. This enables malicious runtime execution, after which the adversary abuses Active Directory Certificate Services through authentication relay and Kerberos. The researchers examine ESC1 and ESC8 vulnerability paths within this chain.
This matters because it shows that social engineering against IT support can cascade into deep infrastructure compromise, turning certificate services into a vector when misconfigured.
What It Means for Readers
Organisations should review how their help desk verifies identity, since the attack abuses legitimate support workflows as an entry point.
What Remains Unknown
Specific mitigation steps are not confirmed in the available excerpt.
VANTIX Takeaway
The confirmed facts show a multi-stage intrusion path from impersonation to certificate abuse, showing that support-channel security can be an entry point to domain compromise.


