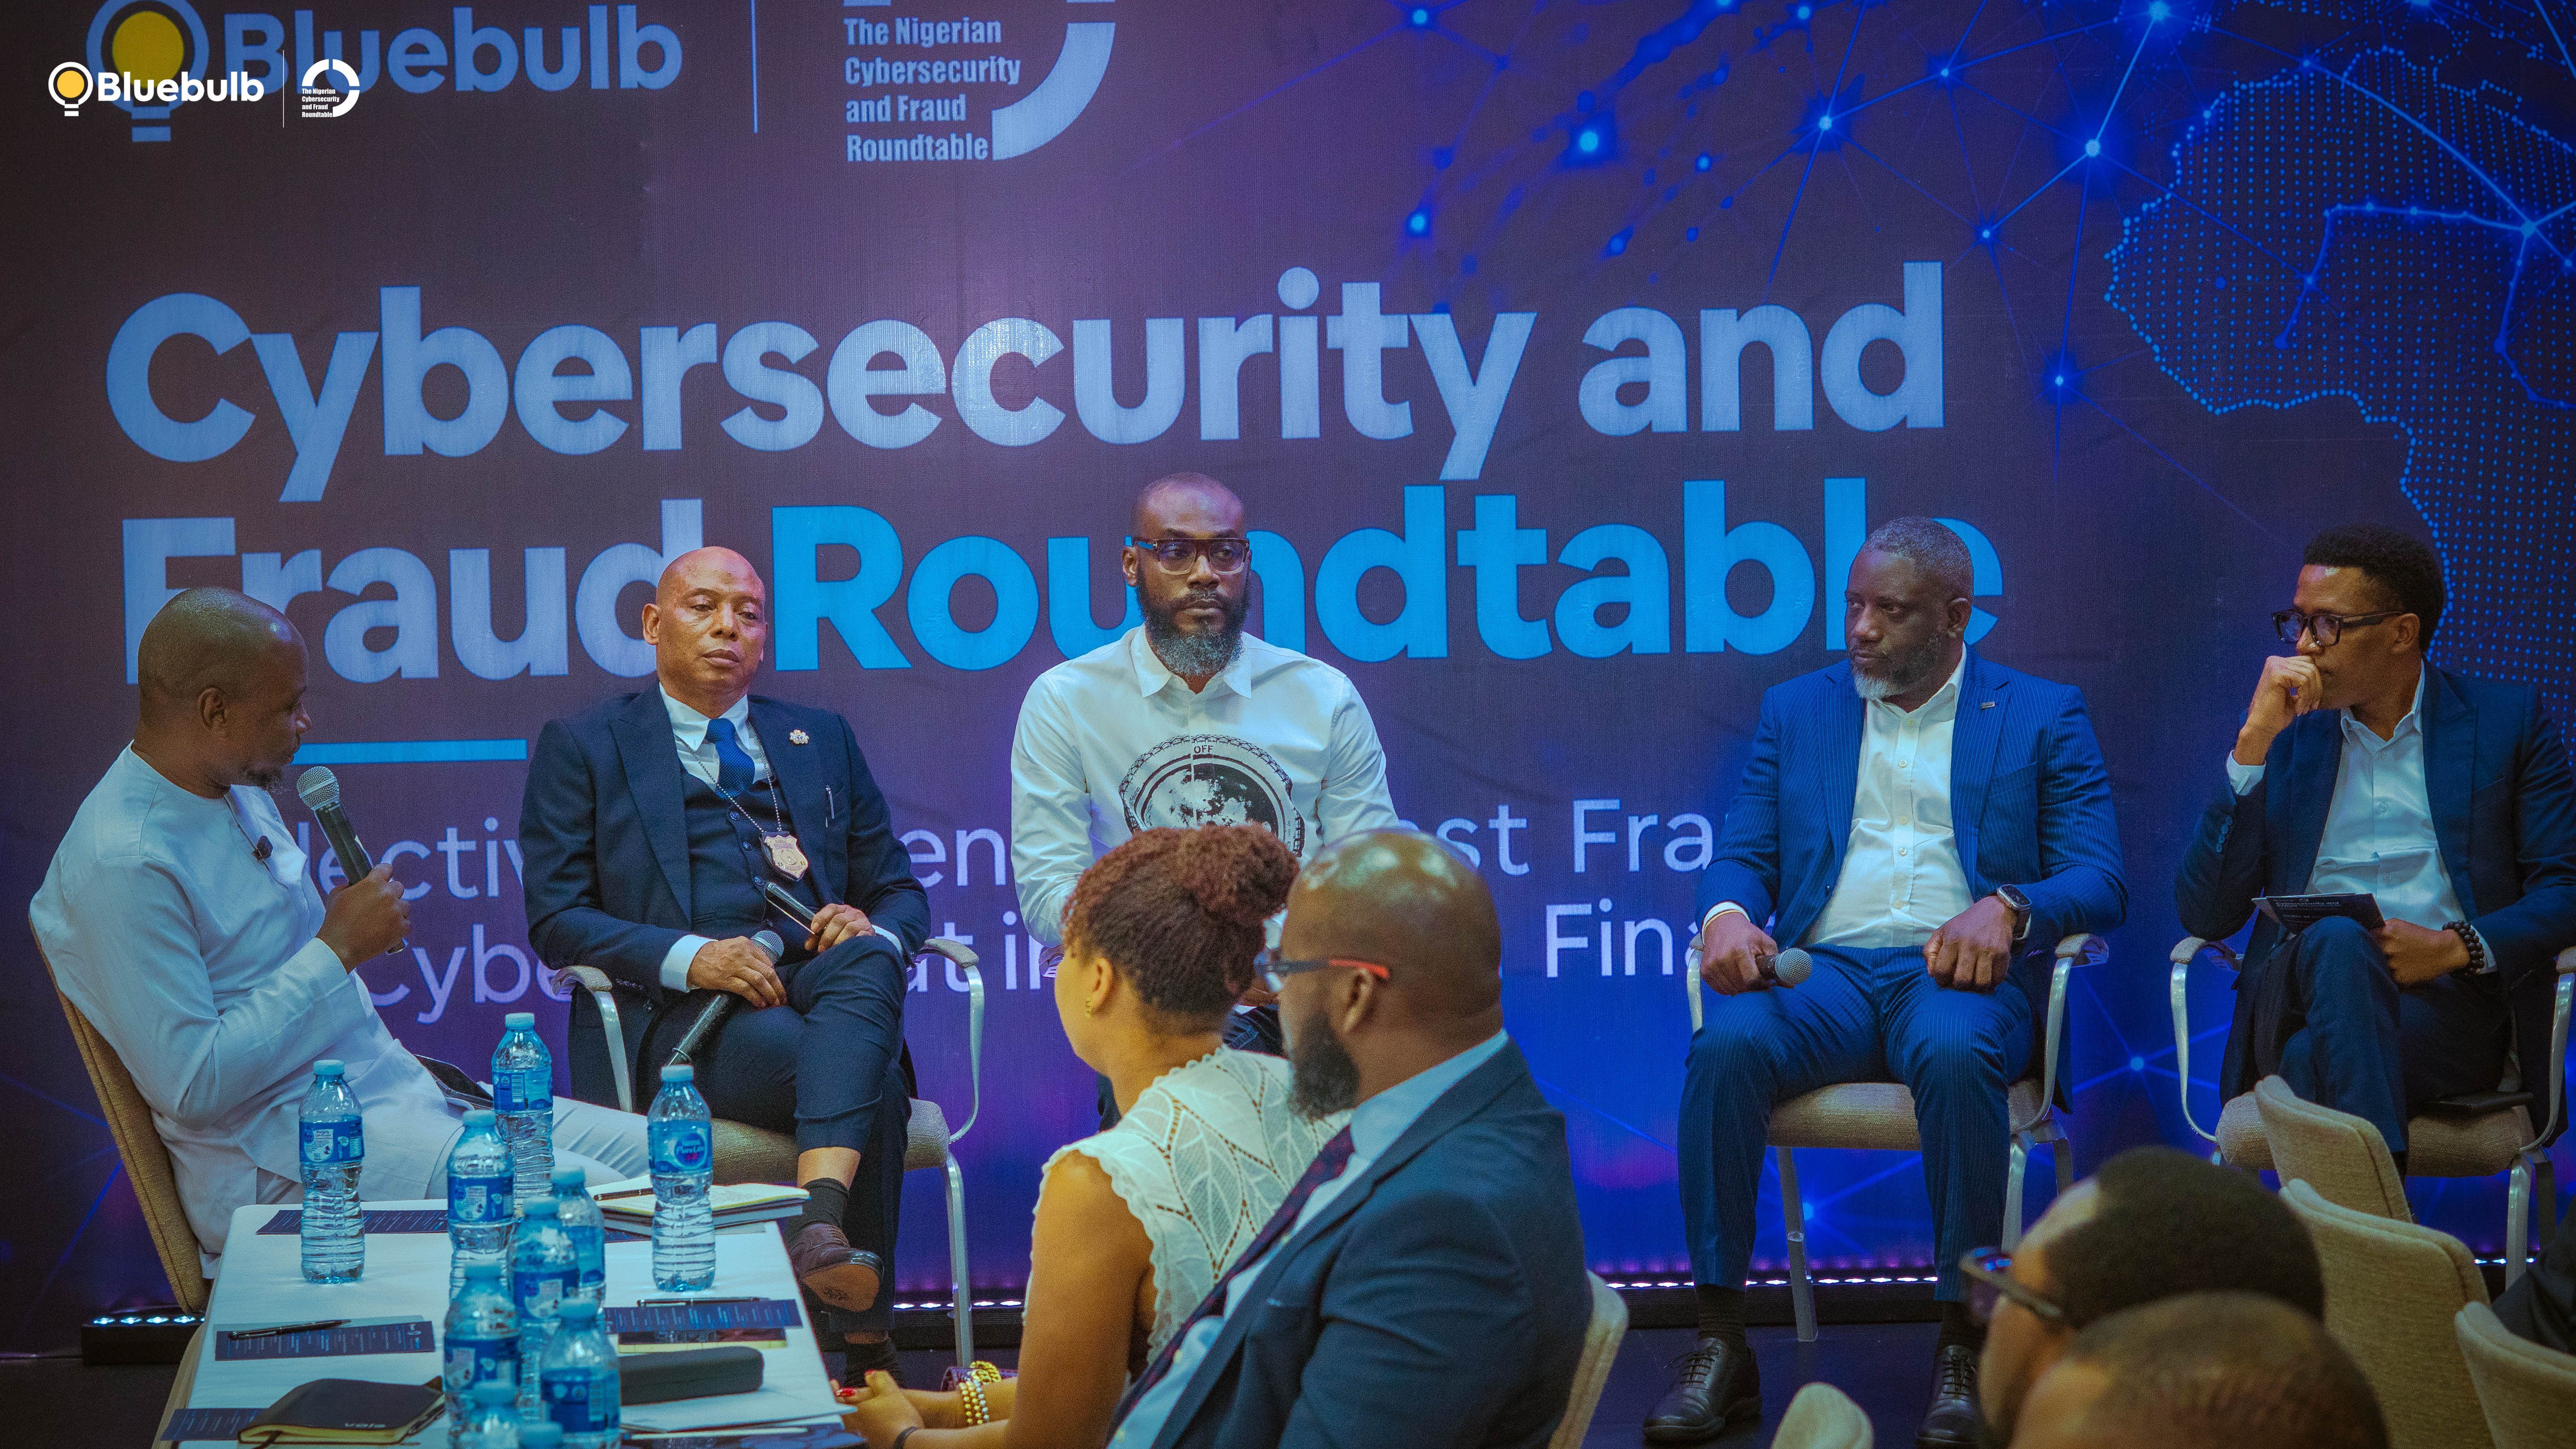
Bluebulb has called for coordinated action against fraud and cyber threats after convening a gathering of industry leaders, according to Technext, which published the report on 12 November 2026 under a byline crediting guest contributor Pelumi Oguntuase.
That is the full extent of what the available record establishes. Only the article's title and byline could be retrieved, so this brief cannot confirm what was discussed, who attended or what came out of the meeting.
What is not yet known
Several details a reader would need are missing:
- What Bluebulb does as a business, and where it operates
- Who the "industry leaders" were, and which sectors they represented
- Where and when the convening took place
- Which specific fraud schemes or cyber threats were named
- Whether any commitments, shared framework or next steps were announced
The problem being referenced
Fraud and cyber threats are often treated as shared problems rather than isolated incidents. A single attack campaign can affect banks, fintech companies, telecoms operators and retailers at the same time, and stolen credentials or customer records frequently move between them. That reasoning underpins the argument for information sharing between companies, regulators and law enforcement, which is a recurring theme in cybersecurity policy discussions.
This paragraph is general background. It is not a description of what Bluebulb proposed or of any position attributed to the company.
Readers who need the specifics of Bluebulb's call, including the participants and any outcomes, will need to consult the full Technext article.


