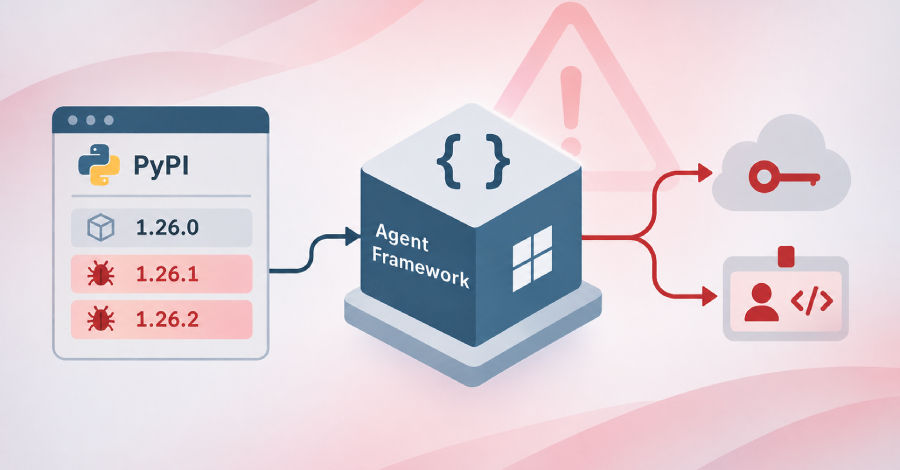
Microsoft's agent-framework package on the Python Package Index (PyPI) was compromised by threat actors who published malicious versions designed to steal cloud credentials, according to reports from multiple security firms.
The malicious versions, numbered 1.26.1 and 1.26.2, were published 33 minutes apart on 17 November 2026. Aikido, Chainguard, Endor Labs, OX Security, SafeDep, Socket, StepSecurity and Google-owned Wiz all reported the incident. The compromised code is designed to run a credential stealer every time Python starts, rather than only when the agent framework itself is used.
PyPI is the official repository where Python developers download software packages. A credential stealer is malware that captures login details, API tokens or passwords stored on an infected machine and sends them to an attacker-controlled server.
Because the malicious code runs on every Python start, any machine that installed versions 1.26.1 or 1.26.2 could be exposed repeatedly, even when the agent framework is not actively running. How many users downloaded the affected versions, whether Microsoft has released fixed versions, and how the attackers gained access to the package remain unknown at the time of reporting.


